Fiat Chrysler offers up to $1,500 for car hacking discoveries
FCA launches a bug bounty programme through Bugcrowd, paying hackers between $150 and $1,500 for reporting cybersecurity flaws in its vehicles and connected services.
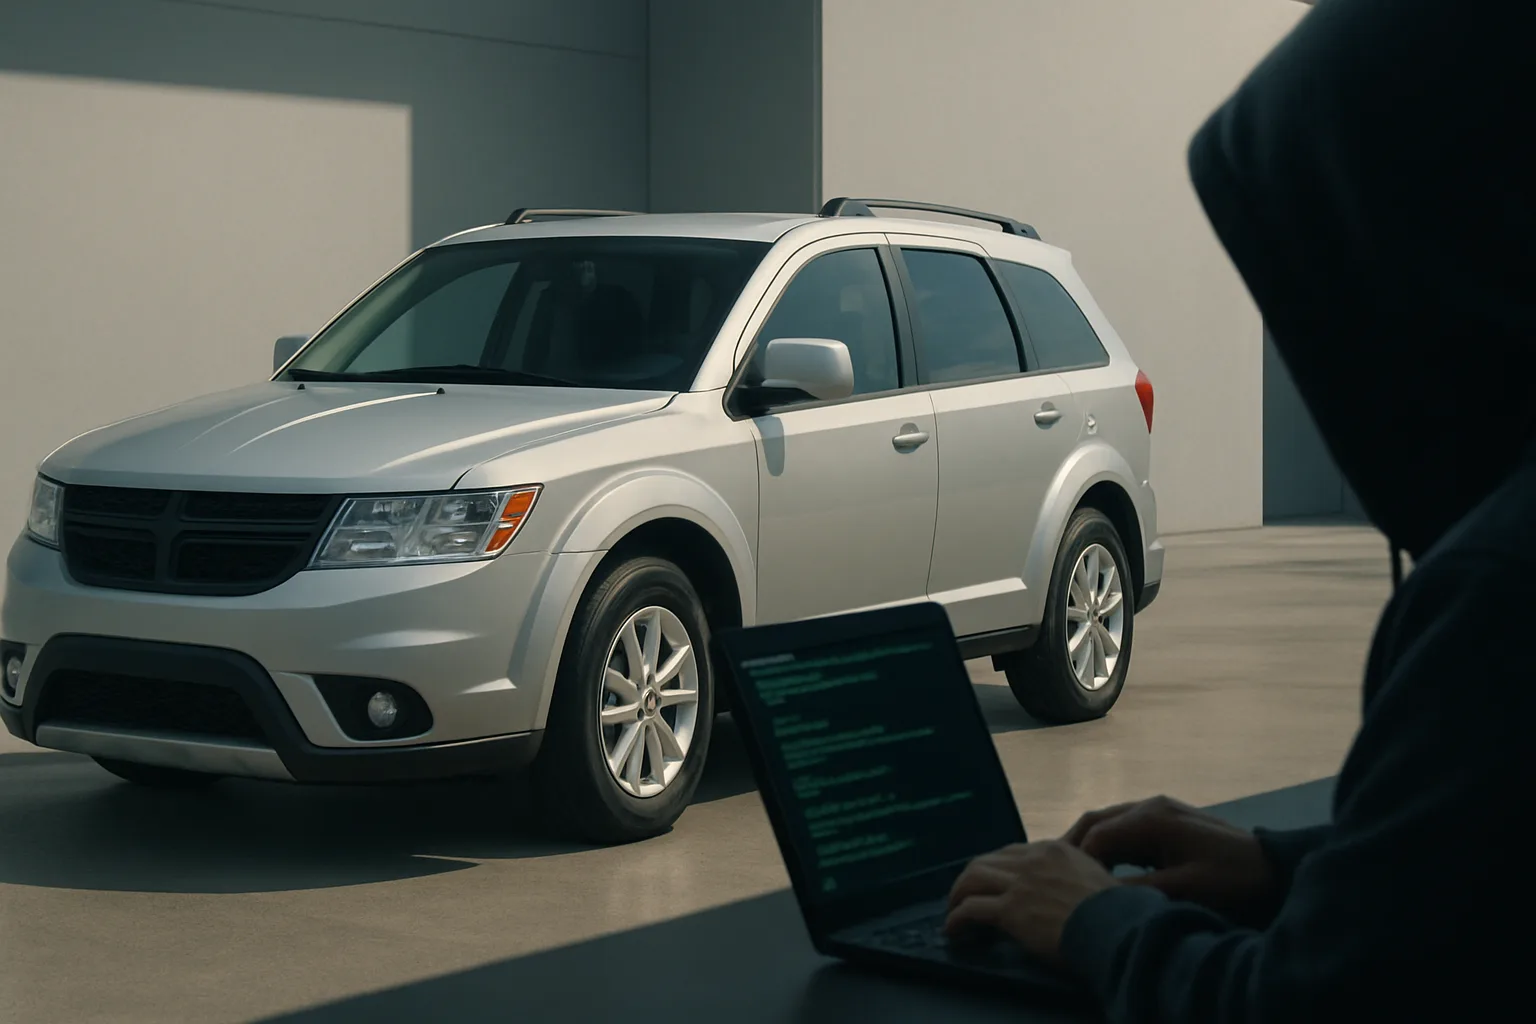
Fiat Chrysler Automobiles (FCA) has launched a public bug bounty programme, offering between $150 and $1,500 to hackers who identify cybersecurity vulnerabilities in its vehicles and connected services. The scheme, announced in July 2016, is managed by Bugcrowd, a platform that runs similar initiatives for technology firms including Tesla.
The move follows growing concern about the risks posed by increasingly connected cars. FCA became the first manufacturer to recall vehicles due to a hacking threat in 2015, after security researchers demonstrated that a Jeep Cherokee could be remotely controlled via its infotainment system. That incident led to a recall of 1.4 million vehicles to address the vulnerability.
How the FCA bug bounty works
The FCA programme invites independent security researchers, often referred to as white-hat hackers, to report flaws they discover in FCA vehicles, mobile apps, or backend systems. The reward depends on the severity and impact of the vulnerability, with the top payout of $1,500 reserved for the most critical findings. Less severe issues can still earn $150 or more.
Bugcrowd acts as the intermediary, vetting submissions before FCA is notified. The company said it wants to encourage responsible disclosure, rather than public exposure of flaws that could put drivers at risk. FCA's security team then works to verify and address the issues, with the aim of patching vulnerabilities before they can be exploited.
Cybersecurity and connected cars
Manufacturers face increasing pressure to secure their vehicles as connectivity expands. Remote access features, over-the-air updates, and integrated apps create new opportunities for hackers to target cars. FCA's decision to pay for bug reports brings it in line with a growing number of technology firms that have adopted similar incentives to crowdsource security testing.
The programme covers all FCA vehicles and connected platforms. Security researchers interested in participating can register through Bugcrowd. FCA has not disclosed how many vulnerabilities have been reported or paid out since the launch, but the company emphasises that cooperation with the wider security community is now a core part of its approach to vehicle safety.